We build security into how the network is designed, changed and run every day, from segmentation and access control to firewall rules you can review, hardening and logging.
When we help
A flat networkEverything reaches everything, and a problem in one place can spread everywhere.
Rules nobody understandsThe firewall grew rule by rule, and nobody knows anymore why they all exist.
Traceability requirementsAccess control and traceable changes for customers, auditors and applicable security requirements, including NIS2.
Security separate from operationsHardening and logging became a project of their own instead of part of daily work.
Every flow with a purpose and an owner
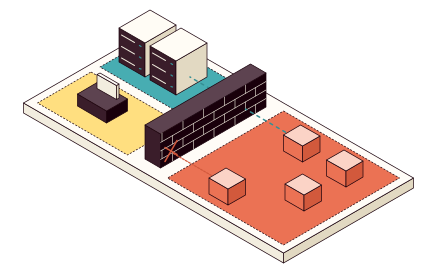
The network is divided by what needs protecting and who needs to reach it, whichever firewalls and switches you run. Every rule between the parts has a purpose you can read and an owner who answers for it.
Divided by what needs protectingSegmentation Divided by what needs protecting Users, guests, servers, management and the systems that run operations get their own segments, with only the flows the business needs between them, described in a segment plan.
Who and what may connectAccess control Who and what may connect Which users and devices reach which segments, for example with 802.1X, and who may administer the network, only from a separate management network.
Rules you can reviewFirewall rules Rules you can review Rules live as code in Git and change through review. You can see why a rule exists, who owns it and when it changed, and rules the traffic no longer needs are removed.
From
To
Allowed
Purpose
Owner
Users
Servers
Web and login
Work in business systems
System owner
Management
Network devices
SSH and API
Operations and changes
Network team
Guests
Internet
Web
Guests reach the internet and nothing else
IT
Users
Management
Nothing
Administration happens only from the management network
Network team
Hardening and logging in daily operations
Security holds when it's part of how the network is run and changed every day.
Hardening by defaultThe same baseline settings on every device, defined in templates, so a new device isn't an exception.
Logging you can useLogins, changes and denied flows are collected in one place, such as your SIEM, and stored off the devices.
Reviewed changesNew rules and changed segments are reviewed, with a history of who changed what and why.
Hardened devicesThe same baseline settings on every device, from templates.
One way inAdministrators log in through a controlled point.
Dedicated management networkKept apart from the users' network. Devices are administered only from here.
Logs in one placeLogins, changes and denied flows, stored off the devices.
Segmentation in stages
An existing network is divided up while the business keeps running. New rules log first, so you can see what they would block before they take effect.
Flow discoveryWhat runs on the network today What the business needs Rules with no known purpose Result Who needs to reach what, and why
Segments and rulesSegments by what needs protecting Rules with a purpose and an owner Management on its own network Result A segment plan and a rule set as code
Log before blockingNew rules log first Unexpected flows are investigated One segment at a time Result Rules tested against real traffic
Enforce and maintainThe rules take effect Changes through review Rules are reviewed regularly Result A network where only the documented flows get through
Rules and segments you can manage
The segment plan, rule set and logging are yours, with the reasons behind every rule. We walk through them together before we leave.
Add a rule through review
Trace a denied flow in the logs
Review the rules for a segment
Segment planThe segments, what they protect and the flows between them.
Rule set as codeEvery rule with its purpose, owner and history.
Logging and alertsWhere the logs are, how long they're kept and what triggers an alert.
RunbooksAdding a rule, adding a segment and investigating a denied flow.
{opacity:0}@media%20(prefers-reduced-motion:no-preference){.iso-flow%3e*{opacity:0;animation:iso-flow%201.2s%20steps(1)%20infinite}.iso-flow%3e:nth-child(2){animation-delay:.4s}.iso-flow%3e:nth-child(3){animation-delay:.8s}}@keyframes%20iso-flow{0%25{opacity:1}33.333%25{opacity:0}}.iso-line{fill:none;stroke-linecap:round;stroke-linejoin:round;vector-effect:non-scaling-stroke}%3c/style%3e%3cg%20transform='scale(.5)'%3e%3cg%20class='iso-box'%3e%3cpath%20d='M-191%2090l368%20212%200%2020%20-368%20-212z'%20fill='%23f2eddf'/%3e%3cpath%20d='M367%20192l-190%20110%200%2020%20190%20-110z'%20fill='%23e2d9c2'/%3e%3cpath%20d='M0%20-20l367%20212%20-190%20110%20-368%20-212z'%20fill='%23fffcf7'/%3e%3c/g%3e%3cg%20class='iso-box'%3e%3cpath%20d='M225%20334l90%2052%200%2016%20-90%20-52z'%20fill='%23f2eddf'/%3e%3cpath%20d='M398%20338l-83%2048%200%2016%2083%20-48z'%20fill='%23e2d9c2'/%3e%3cpath%20d='M308%20286l90%2052%20-83%2048%20-90%20-52z'%20fill='%23fffcf7'/%3e%3c/g%3e%3cpath%20class='iso-floor%20iso-dashed'%20d='M-100%2054l339%20196%20-62%2036%20-340%20-196z'%20fill='%23ffdf8077'/%3e%3cg%20class='iso-flow'%3e%3cpath%20class='iso-line'%20d='M38%2084l-73%2042'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='0'/%3e%3cpath%20class='iso-line'%20d='M38%2084l-73%2042'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='-5'/%3e%3cpath%20class='iso-line'%20d='M38%2084l-73%2042'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='-10'/%3e%3c/g%3e%3cg%20class='iso-flow'%3e%3cpath%20class='iso-line'%20d='M135%20140l-73%2042'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='0'/%3e%3cpath%20class='iso-line'%20d='M135%20140l-73%2042'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='-5'/%3e%3cpath%20class='iso-line'%20d='M135%20140l-73%2042'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='-10'/%3e%3c/g%3e%3cg%20class='iso-flow'%3e%3cpath%20class='iso-line'%20d='M232%20196l-73%2042'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='0'/%3e%3cpath%20class='iso-line'%20d='M232%20196l-73%2042'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='-5'/%3e%3cpath%20class='iso-line'%20d='M232%20196l-73%2042'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='-10'/%3e%3c/g%3e%3cg%20class='iso-flow'%3e%3cpath%20class='iso-line'%20d='M-80%20100l374%20220'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='0'/%3e%3cpath%20class='iso-line'%20d='M-80%20100l374%20220'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='-5'/%3e%3cpath%20class='iso-line'%20d='M-80%20100l374%20220'%20stroke='%23358f94'%20stroke-width='3'%20stroke-dashoffset='-10'/%3e%3c/g%3e%3cg%20class='iso-box'%3e%3cpath%20d='M3%2042l70%2040%200%2024%20-70%20-40z'%20fill='%2347adb2'/%3e%3cpath%20d='M121%2054l-48%2028%200%2024%2048%20-28z'%20fill='%23358f94'/%3e%3cpath%20d='M52%2014l69%2040%20-48%2028%20-70%20-40z'%20fill='%23cfe8e6'/%3e%3c/g%3e%3cg%20class='iso-box'%3e%3cpath%20d='M100%2098l70%2040%200%2024%20-70%20-40z'%20fill='%2347adb2'/%3e%3cpath%20d='M218%20110l-48%2028%200%2024%2048%20-28z'%20fill='%23358f94'/%3e%3cpath%20d='M149%2070l69%2040%20-48%2028%20-70%20-40z'%20fill='%23cfe8e6'/%3e%3c/g%3e%3cg%20class='iso-box'%3e%3cpath%20d='M197%20154l70%2040%200%2024%20-70%20-40z'%20fill='%233a1d2a'/%3e%3cpath%20d='M315%20166l-48%2028%200%2024%2048%20-28z'%20fill='%2319000b'/%3e%3cpath%20d='M246%20126l69%2040%20-48%2028%20-70%20-40z'%20fill='%235d4350'/%3e%3c/g%3e%3cg%20class='iso-box'%3e%3cpath%20d='M-142%2058l38%2022%200%2032%20-38%20-22z'%20fill='%233a1d2a'/%3e%3cpath%20d='M-66%2058l-38%2022%200%2032%2038%20-22z'%20fill='%2319000b'/%3e%3cpath%20d='M-104%2036l38%2022%20-38%2022%20-38%20-22z'%20fill='%235d4350'/%3e%3c/g%3e%3cg%20class='iso-box'%3e%3cpath%20d='M267%20326l48%2028%200%2012%20-48%20-28z'%20fill='%233a1d2a'/%3e%3cpath%20d='M364%20326l-49%2028%200%2012%2049%20-28z'%20fill='%2319000b'/%3e%3cpath%20d='M315%20298l49%2028%20-49%2028%20-48%20-28z'%20fill='%235d4350'/%3e%3c/g%3e%3cg%20class='iso-box'%3e%3cpath%20d='M267%20310l48%2028%200%2012%20-48%20-28z'%20fill='%233a1d2a'/%3e%3cpath%20d='M364%20310l-49%2028%200%2012%2049%20-28z'%20fill='%2319000b'/%3e%3cpath%20d='M315%20282l49%2028%20-49%2028%20-48%20-28z'%20fill='%235d4350'/%3e%3c/g%3e%3cg%20class='iso-box'%3e%3cpath%20d='M267%20294l48%2028%200%2012%20-48%20-28z'%20fill='%233a1d2a'/%3e%3cpath%20d='M364%20294l-49%2028%200%2012%2049%20-28z'%20fill='%2319000b'/%3e%3cpath%20d='M315%20266l49%2028%20-49%2028%20-48%20-28z'%20fill='%235d4350'/%3e%3c/g%3e%3c/g%3e%3c/svg%3e)