Friends Don't Let Friends Share SSH Keys
The era of the bastion host is over. Here's how to get rid of shared SSH keys, exposed jumphosts, and unnecessary complexity.
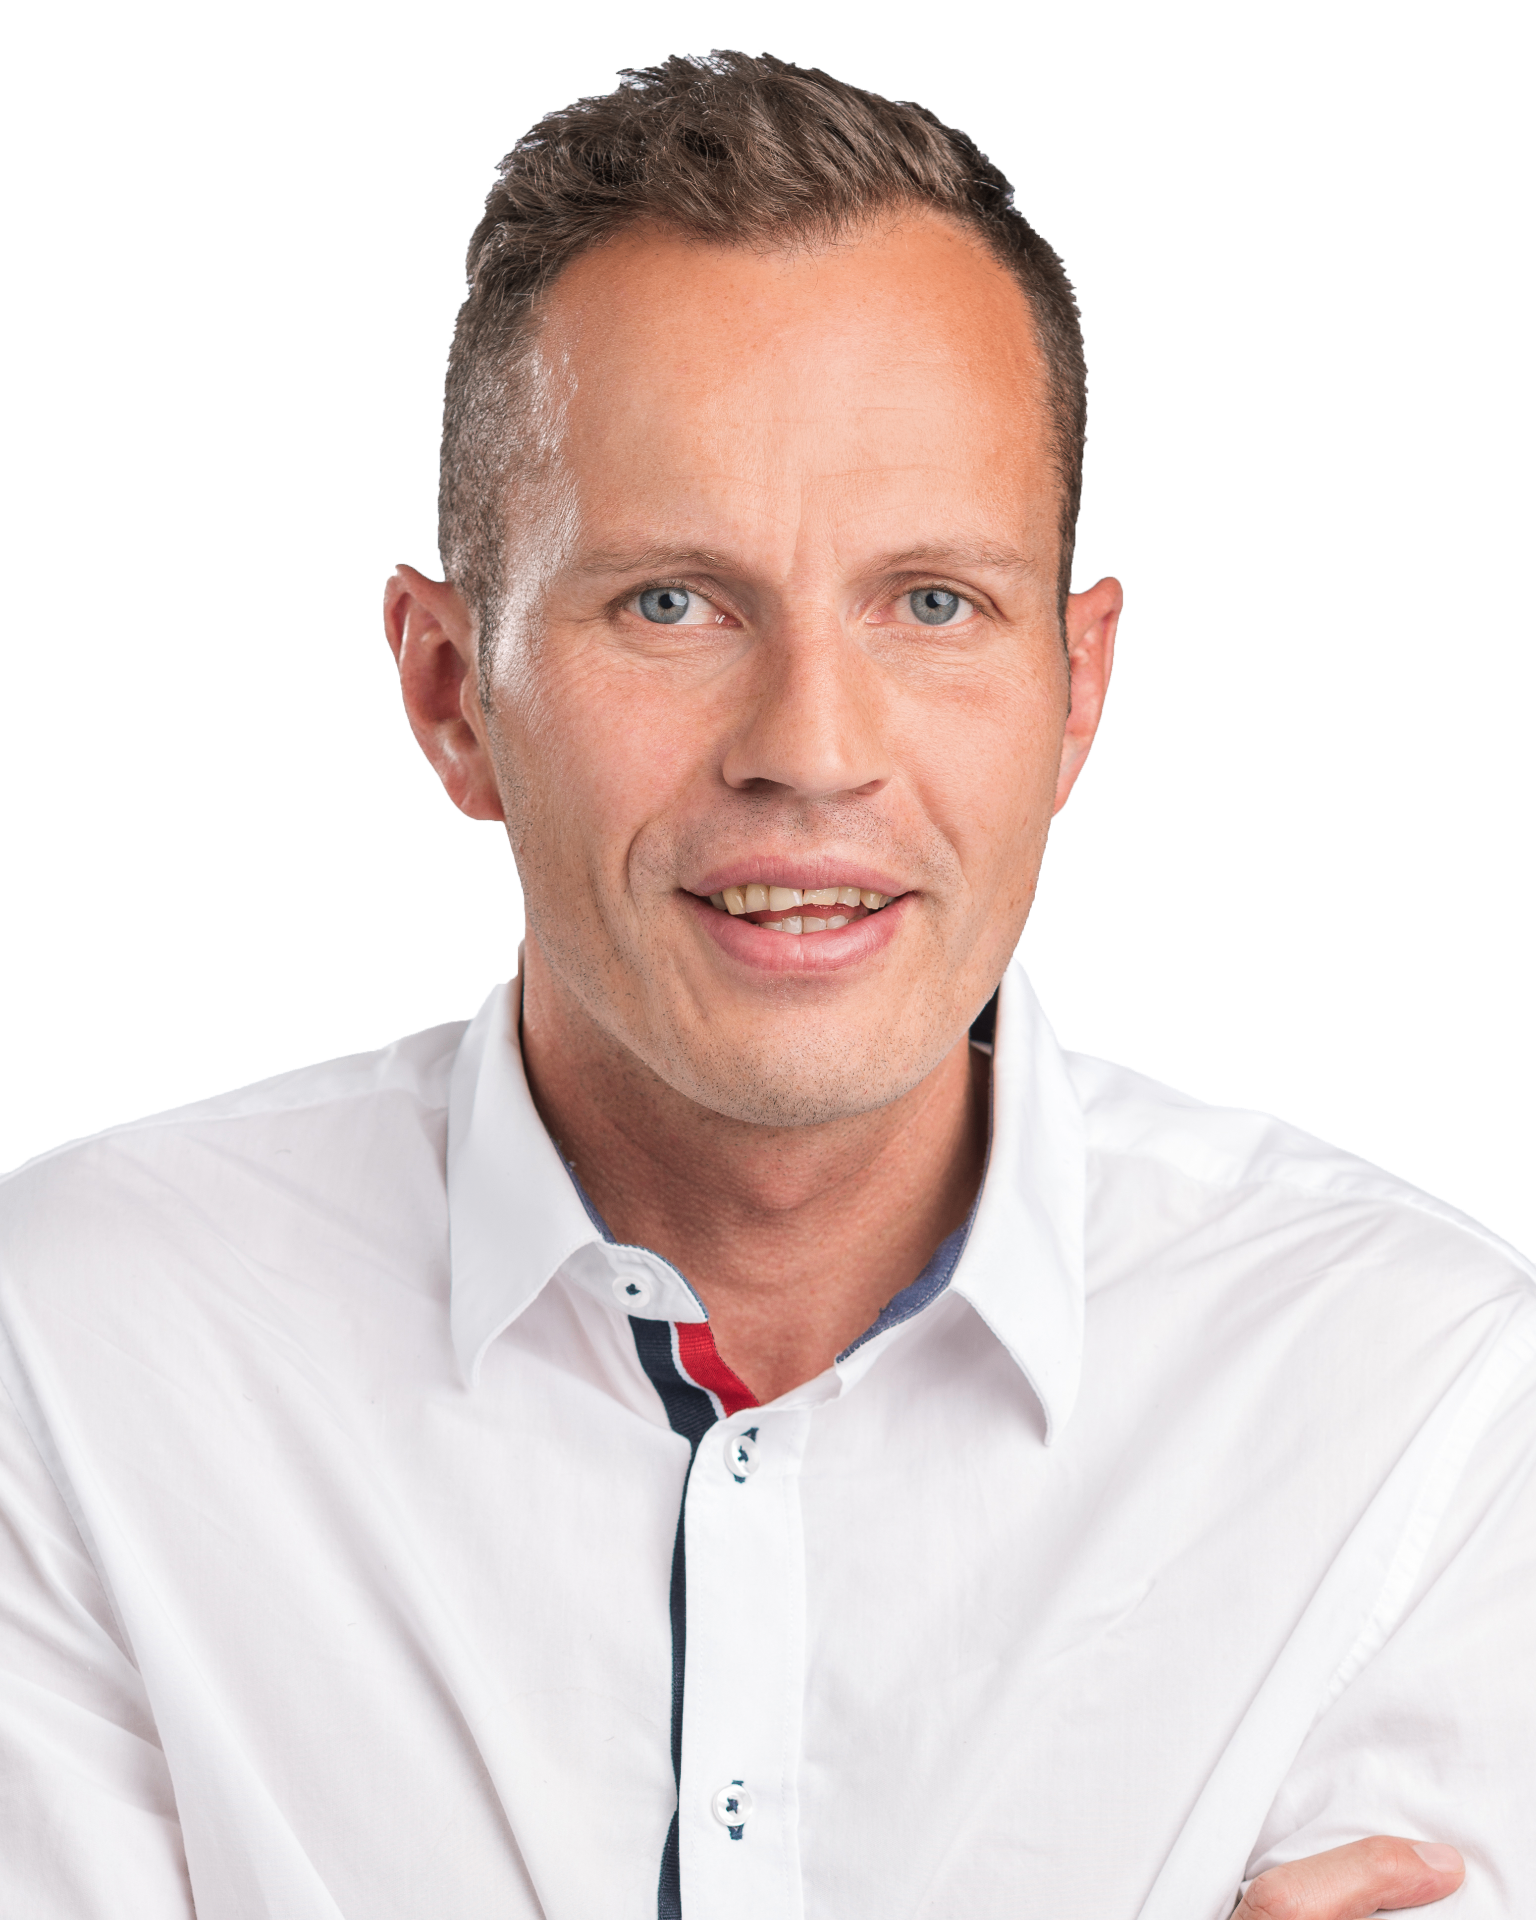
A bastion or jumphost has long been the solution for reaching servers not exposed to the internet. It's time to leave the dinosaurs behind.
Why the bastion model is bad
- You have to expose port 22 to the internet.
- You manage SSH keys – often leading to shared private keys.
- SSH hopping creates cognitive load and complicates file management.
- Logging and access control are often insufficient.
What you should do instead
Identity-based access
Let an identity provider (Okta, Azure AD, Google) control who can log in – not a file with keys.
Short-lived certificates
Use e.g. Teleport, HashiCorp Boundary, or SSH certificates from Vault. The key lives for minutes, not years.
Zero Trust network
Cloudflare Access, Tailscale, or equivalent – access is based on identity + device posture, not on IP.
Full audit trail
All sessions are recorded and linked to a real person. No more anonymous jumphost logs.
Do you want help modernizing your access model? We build it with you.
Security questions around pipelines, access or compliance? I'll make sure the right SecOps consultant reaches out.
Related articles
How to Leave VMware Without Breaking Production
A migration guide for teams that cannot afford downtime: mapping, destination selection, and migration in waves with tested rollback.
Cisco NSO: Why Your Company Needs It – and How to Get Started
Network automation is hot, but where do you begin? We explain why Cisco NSO is often the right tool and how to take the first step.
How to secure your Docker image build pipeline
A robust and secure build process for your Docker containers is a central part of protecting applications in production. Here's how we do it.